 Published by Michael Becker
Last updated on September 21, 2026
•
7 minute read
Ask an OT security lead at any utility why their SCADA network sits behind an air gap, and the answer is almost always the same: because it has to. Substations, generation assets, and the RTUs and PLCs running them are critical infrastructure, and critical infrastructure gets isolated on purpose.
Ask an OT security lead at any utility why their SCADA network sits behind an air gap, and the answer is almost always the same: because it has to. Substations, generation assets, and the RTUs and PLCs running them are critical infrastructure, and critical infrastructure gets isolated on purpose.
IEC 62443, NERC CIP, and NIS2 all push energy operators toward strict zone and conduit models, often mapped against the Purdue Enterprise Reference Architecture, where the deeper a system sits, the less it talks to anything outside its own zone. That isolation is the entire point of the design - and it is also exactly what makes OT network monitoring difficult, because most monitoring platforms quietly assume a live path to the internet that an air-gapped network was built never to have.
Why Is Monitoring an Air-Gapped OT Network So Difficult?
Air-gapped networks block the same connectivity most monitoring tools depend on without ever saying so out loud. No outbound internet access means no cloud dashboard, no automatic license check, no background update - so a platform built around constant connectivity can fail before a single sensor is even configured.
Firewall teams in energy environments have good reason to be strict about this. Opening a broad path from a central monitoring server into a substation network defeats the purpose of the zone in the first place, and an auditor will ask about it sooner or later. So the monitoring tool has to work the other way around: minimal outbound traffic, no inbound rules reaching into process zones, and no dependency on a vendor's cloud service just to keep running day to day. Add several substations or generation sites, each its own isolated cell, and the problem multiplies fast. You are not securing one air gap - you are securing dozens, and every single one of them needs its own answer for how monitoring data gets out without the internet getting in.
Seeing an air-gapped setup in action is easier than explaining it.
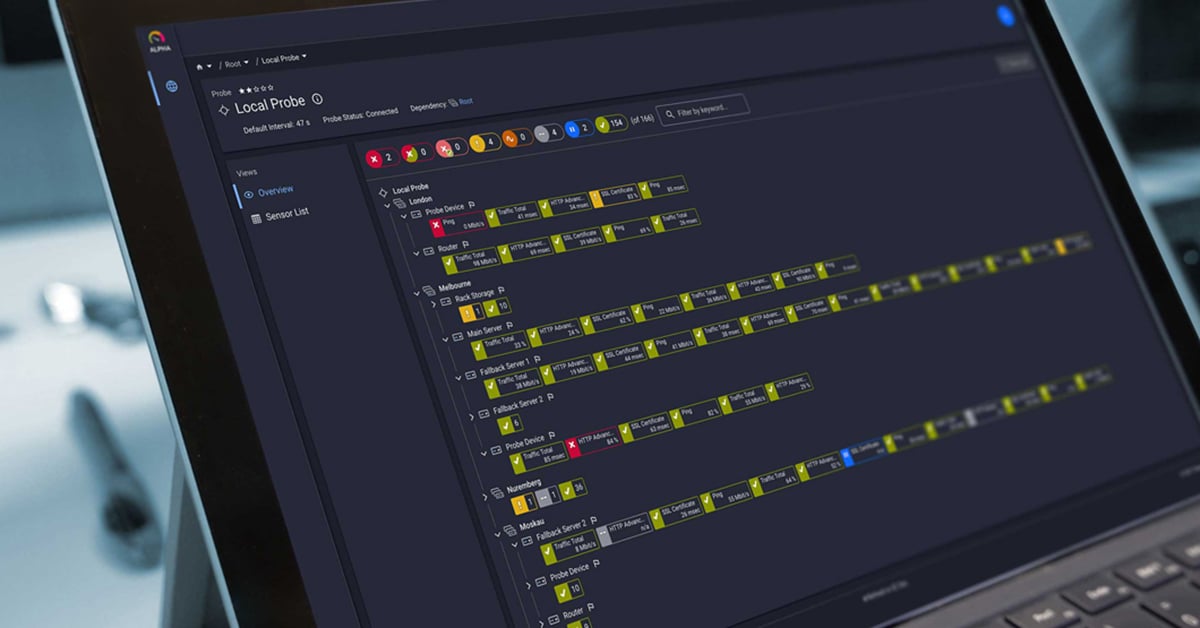
Watch how PRTG Network Monitor collects data across a segmented industrial environment - air gaps included.

How Does PRTG Monitor Networks With No Path to the Internet?
PRTG Network Monitor splits the parts that need connectivity from the parts that do not. A remote probe sits inside each isolated zone, polls devices locally, and sends data to the core server over a single outbound, encrypted connection - one port to document instead of a dozen inbound rules to justify.
The probe always initiates that connection; the core server never reaches back into the zone. For a standard remote probe, that means one TLS-encrypted connection on TCP port 23560. For the multi platform-probe - which also runs on Linux, ARM-based devices such as a Raspberry Pi, or containers on edge hardware, and in some cases directly on PLCs or switches - the same pattern applies over TCP port 23561. This is the same principle behind distributed monitoring in any segmented network: push the polling out to where the devices are, and keep the core server's footprint on the wire as small as possible.
Everything that normally assumes internet access gets switched off instead of tunneled out. License activation runs manually: send the license key and system ID to Paessler's support team by email from a connected machine, then activate offline using the .dat file that comes back. Auto-update gets disabled, and version upgrades turn into a scheduled, tested, offline process rather than a background task nobody signed off on. Notifications route through an internal mail relay or not at all, and anything that resolves an external geolocation or reputation service simply does not apply here. None of this is a workaround bolted onto PRTG Network Monitor after the fact - it is how the deployment is meant to look once it sits inside a segmented industrial network.
Planning your own air-gapped PRTG deployment?
Our best practices whitepaper walks through core server placement, firewall rules, offline licensing, and patch management for isolated OT networks, step by step.

What Does This Look Like in an Energy Environment?
In a typical energy deployment, the PRTG core server sits at Purdue Level 3 or in the industrial DMZ, while a remote probe placed inside each substation or generation zone polls Modbus, OPC UA, and SNMP devices locally and reports back over the one approved conduit.
Picture a distribution utility running dozens of unmanned substations, each with protection relays, RTUs, and a handful of network switches that nobody drives out to check unless something has already gone wrong. A multi-platform probe installed on a small edge device inside the substation zone reads Modbus TCP registers off the relays, checks status through the OPC UA Server where a local historian exists, and keeps an eye on switch health over SNMP - all without exposing a single one of those devices to a network outside the substation. That probe forwards its findings to the core server at Level 3.5, and from there the utility gets one dashboard covering every substation instead of forty separate blind spots.
Where a site is fully air-gapped with genuinely no path out at all, the probe keeps collecting and storing data locally, but full alerting, historical trending, and dashboards still need that connection back to the core through an approved one-way conduit eventually - a data diode is a common choice here. This is close to the exact setup covered on the IT/OT monitoring for energy companies page, where substation and generation-site visibility, alongside NERC CIP, NIS2, and IEC 62443 compliance evidence, is the whole premise.
What Security and Operational Practices Round This Out?
A working air-gapped deployment needs a few operational habits to actually stay air-gapped over time, not just on the day it was installed:
🧩 Keep the probe-to-core conduit rule dedicated to that traffic alone, and never reuse it for any other protocol - it keeps firewall audits straightforward.
🧩 Use least-privilege, read-only accounts for SNMP, Modbus, and database sensors rather than a shared administrative login.
🧩 Back up the core server's configuration and sensor database on the same schedule as other critical OT systems, and actually test the restore instead of assuming the backup works.
Every substation, every PLC, one dashboard - no exceptions.
Watch how PRTG Network Monitor brings SCADA, RTUs, and IT infrastructure together in a single view.
Isolation Without the Blind Spot
None of this is unique to PRTG Network Monitor. Any monitoring platform touching an OT network needs the same discipline around zone placement, narrow conduits, and offline operation - what changes from site to site is the layout: how many substations, how many zones, how strict the air gap actually is. Energy operators dealing with NERC CIP, NIS2, or IEC 62443 audits get a second benefit from the same setup, too: continuous, ready-made evidence that the controls documented on paper are actually running.
For a closer look at how IT and OT visibility comes together on the operations side, the use case on infrastructure monitoring in the energy sector walks through a live example, SCADA systems, remote OT devices, and IT infrastructure included.


 You there!